Mitigating the BEAST, Heartbleed, DROWN and POODLE attacks on SSL/TLS: grade A+
Key points
- Step by step to an A+ on the SSL Labs test: update OpenSSL, configure strong ciphers, add HSTS, then test and verify.
- SSL itself is retired: allow only TLS 1.2 and TLS 1.3, which also closes the doors POODLE, BEAST and DROWN used.
- Heartbleed was an OpenSSL bug: keep OpenSSL on a supported release.
- The TLSRef Configurator (formerly Mozilla’s SSL Configuration Generator) writes a current configuration for you.
Strengthening SSL and TLS Connections: A Step-by-Step Guide
Updated October 2026: SSL itself is retired: SSL 2.0 and SSL 3.0 (the protocol the POODLE attack broke) are long gone, TLS 1.0 and 1.1 were deprecated in 2021 (RFC 8996), and a server today should offer only TLS 1.2 and TLS 1.3. The CentOS and OpenSSL versions in this post have also reached end of life: CentOS Linux 7 in June 2024, OpenSSL 1.1.1 in September 2023 and OpenSSL 3.0 in September 2026. What I recommend now:
- A supported distribution such as AlmaLinux, Rocky Linux or Debian 13, with OpenSSL from its own packages (OpenSSL 3.5 LTS is supported until April 2030). Do not build OpenSSL by hand and link it over the system library, as the old commands below do.
- The TLSRef Configurator (formerly the Mozilla SSL Configuration Generator), intermediate profile, for protocols and ciphers. I added corrected Apache lines after the old code blocks.
- HSTS with
max-age=63072000; includeSubDomainsfor the A+. - The AXIVO repository, the online Heartbleed test and the DROWN test site are gone, and cPanel replaced
/scripts/easyapachewith EasyApache 4 in WHM. On Windows Server, use the Best Practices template of IIS Crypto instead of the old cipher list near the end.
How TLS protects your traffic
TLS (Transport Layer Security), the successor of SSL (Secure Sockets Layer), is the technology used to encrypt and decrypt messages sent between the browser and the server. By encrypting the data, you protect messages from being read while they are transferred across the Internet. TLS encrypts a message from the web browser or application and sends it to the server. When the server receives the message, TLS decrypts it and checks that nobody altered it on the way, and the server proves its identity to the browser with its certificate (a process known as authentication).
It took me a while to understand how to strengthen SSL and TLS connections between the server and clients. Many of us, when performing an SSL test on SSL Labs, receive grades of B, C, or sometimes even F. You can test your own site or trusted sites like e-banking by visiting SSL Labs. If you would like a dedicated test for the Heartbleed attack, use the scanners listed below.
Steps to a grade of A+
In this post, I will explain step by step how to achieve a grade of A+ and mitigate vulnerabilities such as BEAST, Heartbleed, DROWN, and POODLE attacks with a strong choice of ciphers. All you need to do is update your OpenSSL and replace the default settings in your web server configuration file. Here are the steps on CentOS:
- Update OpenSSL: Ensure you have the latest version of OpenSSL installed.
- Configure Strong Ciphers: Replace default ciphers with a stronger selection in your web server configuration.
- Test and Verify:
- Use SSL Labs to test your configuration and ensure you achieve a grade of A+.
- Mitigate known vulnerabilities by following best practices and recommendations.
By following these steps, you can significantly enhance the security of your SSL and TLS connections, providing a safer experience for your users.
Scanners for BEAST, Heartbleed, DROWN and the POODLE attack
- Scan your server for the BEAST attack.
- Scan your server for the Heartbleed attack (Filippo Valsorda’s online Heartbleed test was discontinued in March 2019, and SSL Labs checks it).
- Scan your server for the POODLE attack.
- Scan your server for the DROWN attack (the old test.drownattack.com checker is offline; SSL Labs checks DROWN, and drownattack.com explains the fix).
- Scan your browser’s SSL/TLS support.
- HTTP vs HTTPS to compare load times of the insecure HTTP and encrypted HTTPS versions of a page.
How to fix
To update to OpenSSL version 3 on CentOS:
sudo yum install perl-IPC-Cmd perl-Test-Simple

cd /usr/src
wget https://www.openssl.org/source/openssl-3.0.0.tar.gz
tar -zxf openssl-3.0.0.tar.gz
rm openssl-3.0.0.tar.gz

cd /usr/src/openssl-3.0.0
./config
make
make test
make install

ln -s /usr/local/lib64/libssl.so.3 /usr/lib64/libssl.so.3
ln -s /usr/local/lib64/libcrypto.so.3 /usr/lib64/libcrypto.so.3

openssl version

service httpd restart


# Older versions like 1.1.1:
# First you have to update your OpenSSL manual installation (CentOS 5 or 6):
# I am using openssl-1.1.1g get the latest version number from here.

rpm -qa openssl
yum clean all
yum update "openssl*"
lsof -n | grep ssl | grep DEL
cd /usr/src
wget https://www.openssl.org/source/openssl-1.1.1g.tar.gz
tar -zxf openssl-1.1.1g.tar.gz
cd openssl-1.1.1g
./config --prefix=/usr --openssldir=/usr/local/openssl shared
make
make test
make install
cd /usr/src
rm -rf openssl-1.1.1g.tar.gz
rm -rf openssl-1.1.1g

# Verify that you are running the latest version of OpenSSL:

openssl version

# If you still see the old version please run the following command:

sudo ln -sf /usr/local/ssl/bin/openssl `which openssl`

# Check supported ciphers:

openssl ciphersUpdated October 2026: OpenSSL 3.0.0 above was the first 3.0 release and the whole 3.0 line is now out of support, and the hand-built copy linked into /usr/lib64 replaces the library your distribution patches for you. On AlmaLinux or Rocky Linux, update the packaged OpenSSL instead (on Debian or Ubuntu, use the second pair of lines):
sudo dnf upgrade --refresh openssl openssl-libs
openssl version
sudo systemctl restart httpd

sudo apt update && sudo apt full-upgrade
sudo systemctl restart apache2# You will need to recompile Apache now:
/scripts/easyapache
# Then locate your Web server config file:
locate -s httpd.conf
# Edit the file with nano:
nano /usr/local/apache/conf/httpd.conf
# Search for 'SSLCipherSuite' using CTRL W and replace it with:
# SSL stuff
# This will give rate of 100 on Protocol Support at SSL Labs(Recommended):
SSLProtocol -ALL +TLSv1.2 +TLSv1.3
SSLHonorCipherOrder On
# To get 100 on Cipher Strength and Key Exchange I use this combination of ciphers:
SSLCipherSuite "ECDHE-RSA-AES256-GCM-SHA384 CDHE-ECDSA-AES256-GCM-SHA384 ECDHE-RSA-AES256-SHA384 ECDHE-ECDSA-AES256-SHA384 ECDHE-RSA-AES256-SHA ECDHE-ECDSA-AES256-SHA DHE-DSS-AES256-GCM-SHA384 DHE-RSA-AES256-GCM-SHA384 DHE$
# My preference is to paste all of the above into post_virtualhost_global.conf instead of httpd.conf:
nano /usr/local/apache/conf/includes/post_virtualhost_global.conf
# or
nano /etc/apache2/conf.d/includes/post_virtualhost_2.conf
# So the file would look like this:
# SSL stuff
# This will give rate of 100 on Protocol Support at SSL Labs(Recommended):
SSLProtocol -ALL +TLSv1.2 +TLSv1.3
SSLHonorCipherOrder On
# To get 100 on Cipher Strength and Key Exchange I use this combination of ciphers:
SSLCipherSuite "ECDHE-RSA-AES256-GCM-SHA384 CDHE-ECDSA-AES256-GCM-SHA384 ECDHE-RSA-AES256-SHA384 ECDHE-ECDSA-AES256-SHA384 ECDHE-RSA-AES256-SHA ECDHE-ECDSA-AES256-SHA DHE-DSS-AES256-GCM-SHA384 DHE-RSA-AES256-GCM-SHA384 DHE$
# Compression stuff:
#Add to the end of the file the following:
AddOutputFilterByType DEFLATE text/plain
AddOutputFilterByType DEFLATE text/xml
AddOutputFilterByType DEFLATE application/xhtml+xml
AddOutputFilterByType DEFLATE text/css
AddOutputFilterByType DEFLATE application/xml
AddOutputFilterByType DEFLATE image/svg+xml
AddOutputFilterByType DEFLATE application/rss+xml
AddOutputFilterByType DEFLATE application/atom+xml
AddOutputFilterByType DEFLATE application/x-javascript
AddOutputFilterByType DEFLATE application/x-httpd-php
AddOutputFilterByType DEFLATE application/x-httpd-fastphp
AddOutputFilterByType DEFLATE application/x-httpd-eruby
AddOutputFilterByType DEFLATE text/html
SetOutputFilter DEFLATE
SetEnvIfNoCase Request_URI \.(?:gif|jpe?g|png)$ no-gzip dont-vary
SetEnvIfNoCase Request_URI \.(?:exe|t?gz|zip|bz2|sit|rar)$ no-gzip dont-vary
SetEnvIfNoCase Request_URI \.pdf$ no-gzip dont-vary
SetEnvIfNoCase Request_URI \.avi$ no-gzip dont-vary
SetEnvIfNoCase Request_URI \.mov$ no-gzip dont-vary
SetEnvIfNoCase Request_URI \.mp3$ no-gzip dont-vary
SetEnvIfNoCase Request_URI \.mp4$ no-gzip dont-vary
SetEnvIfNoCase Request_URI \.rm$ no-gzip dont-vary
BrowserMatch ^Mozilla/4 gzip-only-text/html
BrowserMatch ^Mozilla/4\.0[678] no-gzip
BrowserMatch \bMSI[E] !no-gzip !gzip-only-text/html
Header append Vary User-Agent env=!dont-varyUpdated October 2026: The SSLCipherSuite line above was cut off when I copied it out of nano (it ends in DHE$ with no closing quote) and has a typo (CDHE), so it does not set the list it shows. Use these lines from the intermediate profile of the TLSRef Configurator instead (Apache 2.4.36 or later with OpenSSL 1.1.1 or later):
SSLProtocol             -all +TLSv1.2 +TLSv1.3
SSLCipherSuite          ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305
SSLHonorCipherOrder     off
SSLSessionTickets       off
Your score should have grade A now:
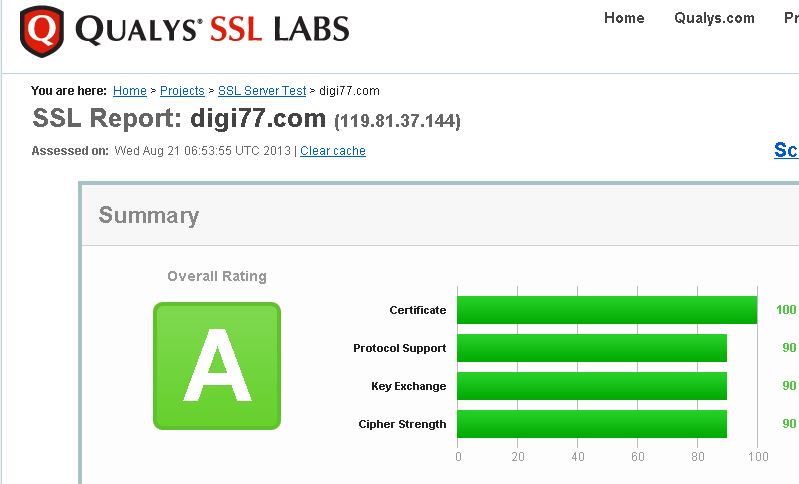
# Up to this level you should get grade A by ssllabs but if you need an A+ then you need to force https for every virtual host you have add this line just after virtual host ip:port

Header always set Strict-Transport-Security "max-age=63072000; includeSubDomains"

# Or do it my way:

nano /usr/local/apache/conf/includes/pre_virtualhost_global.conf

# Paste the following:

        # Use HTTP Strict Transport Security to force client to use secure connections only
        Header always set Strict-Transport-Security "max-age=15768000; includeSubDomains"

# If you would like to exclude all other domains just use the following code:

<If "%{HTTP_HOST} = 'digi77.com'">

        # Use HTTP Strict Transport Security to force client to use secure connections only
        Header always set Strict-Transport-Security "max-age=15768000; includeSubDomains"

<If "%{HTTP_HOST} = 'www.digi77.com'">

        # Use HTTP Strict Transport Security to force client to use secure connections only
        Header always set Strict-Transport-Security "max-age=15768000; includeSubDomains"

# Then let the Webserver force https on all http requests:

# Redirect from http to https
RewriteEngine on
RewriteCond %{HTTPS} off
RewriteRule ^(.*)$ https://%{HTTP_HOST}/$1 [R=301,L]

# Finally, restart your Web server (Apache):

service httpd restartUpdated October 2026: The <If> blocks above lost their closing </If> lines, and the redirect rule above only works as written in a .htaccess file. This is the form the TLSRef Configurator generates (it needs mod_ssl, mod_rewrite and mod_headers); put the HSTS line only in the HTTPS virtual hosts that should send it:
<VirtualHost *:80>
    ServerName www.example.com
    RewriteEngine On
    RewriteCond %{REQUEST_URI} !^/.well-known/acme-challenge/
    RewriteRule ^.*$ https://%{HTTP_HOST}%{REQUEST_URI} [R=301,QSA,L]
</VirtualHost>

<VirtualHost *:443>
    ServerName www.example.com
    SSLEngine on
    SSLCertificateFile      /path/to/signed_cert_and_intermediate_certs
    SSLCertificateKeyFile   /path/to/private_key
    Header always set Strict-Transport-Security "max-age=63072000; includeSubDomains"
</VirtualHost>
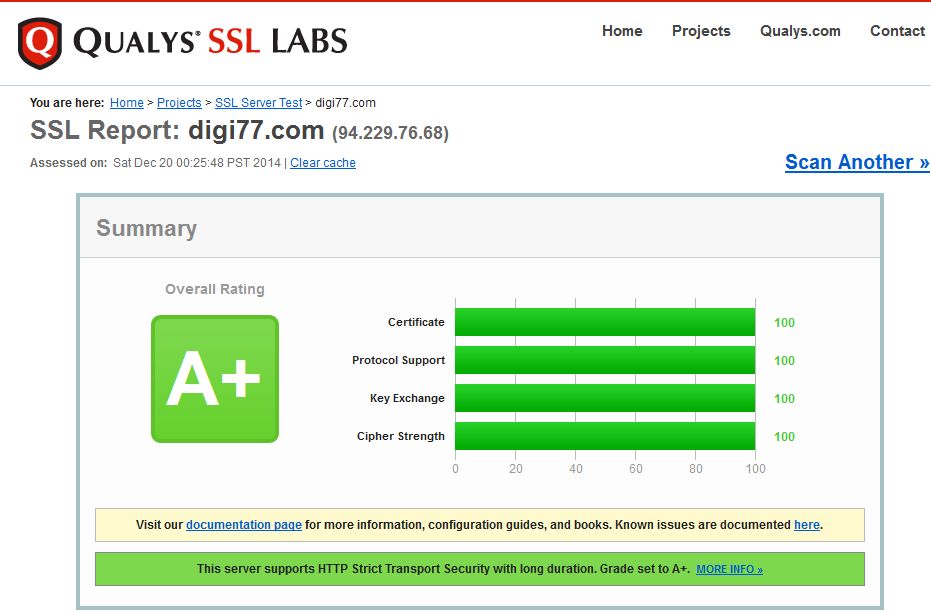
Your score should have grade A+ now:
To mitigate the POODLE attack, I removed SSLv3 support as follows (this line still allows TLS 1.0 and 1.1, which are now deprecated, so use the line below today):
SSLProtocol all -SSLv2 -SSLv3
To get a score of 100 on protocol support, support only TLS 1.2 and TLS 1.3. When I wrote this, TLS 1.2 only was impractical because many clients did not support it; today every current browser supports both:
SSLProtocol -all +TLSv1.2 +TLSv1.3
You can find more Linux commands here.
Extra
TLSRef Configurator (formerly the Mozilla SSL Configuration Generator) here
# If you get this error openssl: error while loading shared libraries: libssl.so.1.1: cannot open shared object file: No such file or directory then

sudo bash -c "echo '/usr/local/lib64' >> /etc/ld.so.conf"
sudo ldconfig

# If you face error while using curl command such as:

# url: (77) Problem with the SSL CA cert (path? access rights?)

# Use the following command to fix it:

yum reinstall ca-certificates

# Adding CAcert root certificate to (Debian/Ubuntu):

sudo mkdir /usr/local/share/ca-certificates/cacert.org
sudo wget -P /usr/local/share/ca-certificates/cacert.org http://www.cacert.org/certs/root.crt http://www.cacert.org/certs/class3.crt
sudo update-ca-certificatesVerbose listing of all OpenSSL ciphers except NULL and anonymous DH, sorted by strength:
openssl ciphers -v 'ALL:!ADH:@STRENGTH'With the OpenSSL 1.0 of that time, the output looked like this (OpenSSL 1.1 and 3 removed the SSLv2, export and Kerberos suites and turn RC4 off by default, so today’s list is much shorter and includes the TLS 1.3 suites):
ECDHE-RSA-AES256-GCM-SHA384 TLSv1.2 Kx=ECDH     Au=RSA  Enc=AESGCM(256) Mac=AEAD
ECDHE-ECDSA-AES256-GCM-SHA384 TLSv1.2 Kx=ECDH     Au=ECDSA Enc=AESGCM(256) Mac=AEAD
ECDHE-RSA-AES256-SHA384 TLSv1.2 Kx=ECDH     Au=RSA  Enc=AES(256)  Mac=SHA384
ECDHE-ECDSA-AES256-SHA384 TLSv1.2 Kx=ECDH     Au=ECDSA Enc=AES(256)  Mac=SHA384
ECDHE-RSA-AES256-SHA    SSLv3 Kx=ECDH     Au=RSA  Enc=AES(256)  Mac=SHA1
ECDHE-ECDSA-AES256-SHA  SSLv3 Kx=ECDH     Au=ECDSA Enc=AES(256)  Mac=SHA1
DHE-DSS-AES256-GCM-SHA384 TLSv1.2 Kx=DH       Au=DSS  Enc=AESGCM(256) Mac=AEAD
DHE-RSA-AES256-GCM-SHA384 TLSv1.2 Kx=DH       Au=RSA  Enc=AESGCM(256) Mac=AEAD
DHE-RSA-AES256-SHA256   TLSv1.2 Kx=DH       Au=RSA  Enc=AES(256)  Mac=SHA256
DHE-DSS-AES256-SHA256   TLSv1.2 Kx=DH       Au=DSS  Enc=AES(256)  Mac=SHA256
DHE-RSA-AES256-SHA      SSLv3 Kx=DH       Au=RSA  Enc=AES(256)  Mac=SHA1
DHE-DSS-AES256-SHA      SSLv3 Kx=DH       Au=DSS  Enc=AES(256)  Mac=SHA1
DHE-RSA-CAMELLIA256-SHA SSLv3 Kx=DH       Au=RSA  Enc=Camellia(256) Mac=SHA1
DHE-DSS-CAMELLIA256-SHA SSLv3 Kx=DH       Au=DSS  Enc=Camellia(256) Mac=SHA1
AECDH-AES256-SHA        SSLv3 Kx=ECDH     Au=None Enc=AES(256)  Mac=SHA1
ECDH-RSA-AES256-GCM-SHA384 TLSv1.2 Kx=ECDH/RSA Au=ECDH Enc=AESGCM(256) Mac=AEAD
ECDH-ECDSA-AES256-GCM-SHA384 TLSv1.2 Kx=ECDH/ECDSA Au=ECDH Enc=AESGCM(256) Mac=AEAD
ECDH-RSA-AES256-SHA384  TLSv1.2 Kx=ECDH/RSA Au=ECDH Enc=AES(256)  Mac=SHA384
ECDH-ECDSA-AES256-SHA384 TLSv1.2 Kx=ECDH/ECDSA Au=ECDH Enc=AES(256)  Mac=SHA384
ECDH-RSA-AES256-SHA     SSLv3 Kx=ECDH/RSA Au=ECDH Enc=AES(256)  Mac=SHA1
ECDH-ECDSA-AES256-SHA   SSLv3 Kx=ECDH/ECDSA Au=ECDH Enc=AES(256)  Mac=SHA1
AES256-GCM-SHA384       TLSv1.2 Kx=RSA      Au=RSA  Enc=AESGCM(256) Mac=AEAD
AES256-SHA256           TLSv1.2 Kx=RSA      Au=RSA  Enc=AES(256)  Mac=SHA256
AES256-SHA              SSLv3 Kx=RSA      Au=RSA  Enc=AES(256)  Mac=SHA1
CAMELLIA256-SHA         SSLv3 Kx=RSA      Au=RSA  Enc=Camellia(256) Mac=SHA1
PSK-AES256-CBC-SHA      SSLv3 Kx=PSK      Au=PSK  Enc=AES(256)  Mac=SHA1
ECDHE-RSA-AES128-GCM-SHA256 TLSv1.2 Kx=ECDH     Au=RSA  Enc=AESGCM(128) Mac=AEAD
ECDHE-ECDSA-AES128-GCM-SHA256 TLSv1.2 Kx=ECDH     Au=ECDSA Enc=AESGCM(128) Mac=AEAD
ECDHE-RSA-AES128-SHA256 TLSv1.2 Kx=ECDH     Au=RSA  Enc=AES(128)  Mac=SHA256
ECDHE-ECDSA-AES128-SHA256 TLSv1.2 Kx=ECDH     Au=ECDSA Enc=AES(128)  Mac=SHA256
ECDHE-RSA-AES128-SHA    SSLv3 Kx=ECDH     Au=RSA  Enc=AES(128)  Mac=SHA1
ECDHE-ECDSA-AES128-SHA  SSLv3 Kx=ECDH     Au=ECDSA Enc=AES(128)  Mac=SHA1
DHE-DSS-AES128-GCM-SHA256 TLSv1.2 Kx=DH       Au=DSS  Enc=AESGCM(128) Mac=AEAD
DHE-RSA-AES128-GCM-SHA256 TLSv1.2 Kx=DH       Au=RSA  Enc=AESGCM(128) Mac=AEAD
DHE-RSA-AES128-SHA256   TLSv1.2 Kx=DH       Au=RSA  Enc=AES(128)  Mac=SHA256
DHE-DSS-AES128-SHA256   TLSv1.2 Kx=DH       Au=DSS  Enc=AES(128)  Mac=SHA256
DHE-RSA-AES128-SHA      SSLv3 Kx=DH       Au=RSA  Enc=AES(128)  Mac=SHA1
DHE-DSS-AES128-SHA      SSLv3 Kx=DH       Au=DSS  Enc=AES(128)  Mac=SHA1
ECDHE-RSA-DES-CBC3-SHA  SSLv3 Kx=ECDH     Au=RSA  Enc=3DES(168) Mac=SHA1
ECDHE-ECDSA-DES-CBC3-SHA SSLv3 Kx=ECDH     Au=ECDSA Enc=3DES(168) Mac=SHA1
DHE-RSA-SEED-SHA        SSLv3 Kx=DH       Au=RSA  Enc=SEED(128) Mac=SHA1
DHE-DSS-SEED-SHA        SSLv3 Kx=DH       Au=DSS  Enc=SEED(128) Mac=SHA1
DHE-RSA-CAMELLIA128-SHA SSLv3 Kx=DH       Au=RSA  Enc=Camellia(128) Mac=SHA1
DHE-DSS-CAMELLIA128-SHA SSLv3 Kx=DH       Au=DSS  Enc=Camellia(128) Mac=SHA1
EDH-RSA-DES-CBC3-SHA    SSLv3 Kx=DH       Au=RSA  Enc=3DES(168) Mac=SHA1
EDH-DSS-DES-CBC3-SHA    SSLv3 Kx=DH       Au=DSS  Enc=3DES(168) Mac=SHA1
AECDH-AES128-SHA        SSLv3 Kx=ECDH     Au=None Enc=AES(128)  Mac=SHA1
AECDH-DES-CBC3-SHA      SSLv3 Kx=ECDH     Au=None Enc=3DES(168) Mac=SHA1
ECDH-RSA-AES128-GCM-SHA256 TLSv1.2 Kx=ECDH/RSA Au=ECDH Enc=AESGCM(128) Mac=AEAD
ECDH-ECDSA-AES128-GCM-SHA256 TLSv1.2 Kx=ECDH/ECDSA Au=ECDH Enc=AESGCM(128) Mac=AEAD
ECDH-RSA-AES128-SHA256  TLSv1.2 Kx=ECDH/RSA Au=ECDH Enc=AES(128)  Mac=SHA256
ECDH-ECDSA-AES128-SHA256 TLSv1.2 Kx=ECDH/ECDSA Au=ECDH Enc=AES(128)  Mac=SHA256
ECDH-RSA-AES128-SHA     SSLv3 Kx=ECDH/RSA Au=ECDH Enc=AES(128)  Mac=SHA1
ECDH-ECDSA-AES128-SHA   SSLv3 Kx=ECDH/ECDSA Au=ECDH Enc=AES(128)  Mac=SHA1
ECDH-RSA-DES-CBC3-SHA   SSLv3 Kx=ECDH/RSA Au=ECDH Enc=3DES(168) Mac=SHA1
ECDH-ECDSA-DES-CBC3-SHA SSLv3 Kx=ECDH/ECDSA Au=ECDH Enc=3DES(168) Mac=SHA1
AES128-GCM-SHA256       TLSv1.2 Kx=RSA      Au=RSA  Enc=AESGCM(128) Mac=AEAD
AES128-SHA256           TLSv1.2 Kx=RSA      Au=RSA  Enc=AES(128)  Mac=SHA256
AES128-SHA              SSLv3 Kx=RSA      Au=RSA  Enc=AES(128)  Mac=SHA1
SEED-SHA                SSLv3 Kx=RSA      Au=RSA  Enc=SEED(128) Mac=SHA1
CAMELLIA128-SHA         SSLv3 Kx=RSA      Au=RSA  Enc=Camellia(128) Mac=SHA1
DES-CBC3-SHA            SSLv3 Kx=RSA      Au=RSA  Enc=3DES(168) Mac=SHA1
IDEA-CBC-SHA            SSLv3 Kx=RSA      Au=RSA  Enc=IDEA(128) Mac=SHA1
DES-CBC3-MD5            SSLv2 Kx=RSA      Au=RSA  Enc=3DES(168) Mac=MD5
IDEA-CBC-MD5            SSLv2 Kx=RSA      Au=RSA  Enc=IDEA(128) Mac=MD5
RC2-CBC-MD5             SSLv2 Kx=RSA      Au=RSA  Enc=RC2(128)  Mac=MD5
PSK-AES128-CBC-SHA      SSLv3 Kx=PSK      Au=PSK  Enc=AES(128)  Mac=SHA1
PSK-3DES-EDE-CBC-SHA    SSLv3 Kx=PSK      Au=PSK  Enc=3DES(168) Mac=SHA1
KRB5-IDEA-CBC-SHA       SSLv3 Kx=KRB5     Au=KRB5 Enc=IDEA(128) Mac=SHA1
KRB5-DES-CBC3-SHA       SSLv3 Kx=KRB5     Au=KRB5 Enc=3DES(168) Mac=SHA1
KRB5-IDEA-CBC-MD5       SSLv3 Kx=KRB5     Au=KRB5 Enc=IDEA(128) Mac=MD5
KRB5-DES-CBC3-MD5       SSLv3 Kx=KRB5     Au=KRB5 Enc=3DES(168) Mac=MD5
ECDHE-RSA-RC4-SHA       SSLv3 Kx=ECDH     Au=RSA  Enc=RC4(128)  Mac=SHA1
ECDHE-ECDSA-RC4-SHA     SSLv3 Kx=ECDH     Au=ECDSA Enc=RC4(128)  Mac=SHA1
AECDH-RC4-SHA           SSLv3 Kx=ECDH     Au=None Enc=RC4(128)  Mac=SHA1
ECDH-RSA-RC4-SHA        SSLv3 Kx=ECDH/RSA Au=ECDH Enc=RC4(128)  Mac=SHA1
ECDH-ECDSA-RC4-SHA      SSLv3 Kx=ECDH/ECDSA Au=ECDH Enc=RC4(128)  Mac=SHA1
RC4-SHA                 SSLv3 Kx=RSA      Au=RSA  Enc=RC4(128)  Mac=SHA1
RC4-MD5                 SSLv3 Kx=RSA      Au=RSA  Enc=RC4(128)  Mac=MD5
RC4-MD5                 SSLv2 Kx=RSA      Au=RSA  Enc=RC4(128)  Mac=MD5
PSK-RC4-SHA             SSLv3 Kx=PSK      Au=PSK  Enc=RC4(128)  Mac=SHA1
KRB5-RC4-SHA            SSLv3 Kx=KRB5     Au=KRB5 Enc=RC4(128)  Mac=SHA1
KRB5-RC4-MD5            SSLv3 Kx=KRB5     Au=KRB5 Enc=RC4(128)  Mac=MD5
EDH-RSA-DES-CBC-SHA     SSLv3 Kx=DH       Au=RSA  Enc=DES(56)   Mac=SHA1
EDH-DSS-DES-CBC-SHA     SSLv3 Kx=DH       Au=DSS  Enc=DES(56)   Mac=SHA1
DES-CBC-SHA             SSLv3 Kx=RSA      Au=RSA  Enc=DES(56)   Mac=SHA1
DES-CBC-MD5             SSLv2 Kx=RSA      Au=RSA  Enc=DES(56)   Mac=MD5
KRB5-DES-CBC-SHA        SSLv3 Kx=KRB5     Au=KRB5 Enc=DES(56)   Mac=SHA1
KRB5-DES-CBC-MD5        SSLv3 Kx=KRB5     Au=KRB5 Enc=DES(56)   Mac=MD5
EXP-EDH-RSA-DES-CBC-SHA SSLv3 Kx=DH(512)  Au=RSA  Enc=DES(40)   Mac=SHA1 export
EXP-EDH-DSS-DES-CBC-SHA SSLv3 Kx=DH(512)  Au=DSS  Enc=DES(40)   Mac=SHA1 export
EXP-DES-CBC-SHA         SSLv3 Kx=RSA(512) Au=RSA  Enc=DES(40)   Mac=SHA1 export
EXP-RC2-CBC-MD5         SSLv3 Kx=RSA(512) Au=RSA  Enc=RC2(40)   Mac=MD5  export
EXP-RC2-CBC-MD5         SSLv2 Kx=RSA(512) Au=RSA  Enc=RC2(40)   Mac=MD5  export
EXP-KRB5-RC2-CBC-SHA    SSLv3 Kx=KRB5     Au=KRB5 Enc=RC2(40)   Mac=SHA1 export
EXP-KRB5-DES-CBC-SHA    SSLv3 Kx=KRB5     Au=KRB5 Enc=DES(40)   Mac=SHA1 export
EXP-KRB5-RC2-CBC-MD5    SSLv3 Kx=KRB5     Au=KRB5 Enc=RC2(40)   Mac=MD5  export
EXP-KRB5-DES-CBC-MD5    SSLv3 Kx=KRB5     Au=KRB5 Enc=DES(40)   Mac=MD5  export
EXP-RC4-MD5             SSLv3 Kx=RSA(512) Au=RSA  Enc=RC4(40)   Mac=MD5  export
EXP-RC4-MD5             SSLv2 Kx=RSA(512) Au=RSA  Enc=RC4(40)   Mac=MD5  export
EXP-KRB5-RC4-SHA        SSLv3 Kx=KRB5     Au=KRB5 Enc=RC4(40)   Mac=SHA1 export
EXP-KRB5-RC4-MD5        SSLv3 Kx=KRB5     Au=KRB5 Enc=RC4(40)   Mac=MD5  export

# For Windows Server Admins, here's the optimal ordered and curated cipher suite by Steve Gibson:

TLS_ECDHE_ECDSA_WITH_AES_256_GCM_SHA384_P384,
TLS_ECDHE_ECDSA_WITH_AES_256_CBC_SHA_P384,
TLS_ECDHE_RSA_WITH_AES_256_CBC_SHA_P384,
TLS_ECDHE_ECDSA_WITH_AES_256_CBC_SHA_P256,
TLS_ECDHE_RSA_WITH_AES_256_CBC_SHA_P256,
TLS_ECDHE_ECDSA_WITH_AES_128_GCM_SHA256_P384,
TLS_ECDHE_ECDSA_WITH_AES_128_CBC_SHA256_P384,
TLS_ECDHE_ECDSA_WITH_AES_128_GCM_SHA256_P256,
TLS_ECDHE_ECDSA_WITH_AES_128_CBC_SHA256_P256,
TLS_ECDHE_ECDSA_WITH_AES_128_CBC_SHA_P384,
TLS_ECDHE_ECDSA_WITH_AES_128_CBC_SHA_P256,
TLS_ECDHE_RSA_WITH_AES_128_CBC_SHA_P384,
TLS_ECDHE_RSA_WITH_AES_128_CBC_SHA_P256,
TLS_ECDHE_RSA_WITH_AES_128_CBC_SHA256_P384,
TLS_ECDHE_RSA_WITH_AES_128_CBC_SHA256_P256,
TLS_DHE_DSS_WITH_AES_256_CBC_SHA256,
TLS_DHE_DSS_WITH_AES_256_CBC_SHA,
TLS_DHE_DSS_WITH_AES_128_CBC_SHA256,
TLS_DHE_DSS_WITH_AES_128_CBC_SHA,
TLS_DHE_DSS_WITH_3DES_EDE_CBC_SHA,
TLS_RSA_WITH_AES_256_CBC_SHA256,
TLS_RSA_WITH_AES_256_CBC_SHA,
TLS_RSA_WITH_AES_128_CBC_SHA256,
TLS_RSA_WITH_AES_128_CBC_SHA,
TLS_RSA_WITH_3DES_EDE_CBC_SHA,
SSL_CK_DES_192_EDE3_CBC_WITH_MD5

# The following are auto update commands on CentOS but you won't get the latest version:

#Enterprise Linux 6
sudo rpm -ivh --nosignature http://rpm.axivo.com/axivo-release-6-1.noarch.rpm
#Enterprise Linux 7
sudo rpm -ivh --nosignature http://rpm.axivo.com/axivo-release-7-1.noarch.rpm
yum --enablerepo=axivo update openssl

# Or install it if not installed :

sudo rpm -ivh --nosignature http://rpm.axivo.com/axivo-release-7-1.noarch.rpm
yum --enablerepo=axivo install opensslThe AXIVO repository used by the last commands above has closed (rpm.axivo.com no longer resolves and axivo.com/packages/setup redirects to the home page), so skip those commands and use your distribution’s own OpenSSL packages.