SSL Evaluation for Oman Local Banks
Key points
- In my tests (the last on 5 November 2016), most Oman banks fell short of the A grade online banking needs on the Qualys SSL Labs server test.
- What I recommended: new certificates with strong keys, and ciphers that support forward secrecy.
- These grades measure one thing only, the connection between your browser and the bank, and say nothing about how the banks are set up today: check any bank yourself with the free SSL Labs test.
We all know that any bank offering online banking services should prioritize their customers’ security concerns. It was disappointing to discover that most local Oman banks are unaware of their SSL grades, which could pose a significant threat to both the banks and their clients. Below, I will list some of these banks along with recommendations on how to address these issues.
If you are associated with any of these entities, please ensure that your security teams are informed and take action. If they encounter difficulties, do not hesitate to contact me. This may seem like a simple matter, but I am confident it could lead to security breaches in the near future. Enhancing security is our national duty.
Before we start, please note that I have previously published a tutorial on how to solve SSL issues and obtain an A+ grade; you can find it here. Banking security specialists, feel free to make use of it.
Overall rating scheme (latest test on 5 November 2016)
Updated October 2026: The grades below are from my last test on 5 November 2016 and say nothing about how these banks are set up today. You can check any bank yourself with the free SSL Labs Server Test. TLS practice has also moved on since I wrote this:
- TLS 1.0 and 1.1 are deprecated (RFC 8996, 2021) and the major browsers dropped them in 2020; SSL Labs caps any server that still offers them at grade B. Offer TLS 1.3 and TLS 1.2 only, with ECDHE key exchange and AEAD ciphers (AES-GCM or ChaCha20-Poly1305).
- An RSA 2048-bit or ECDSA P-256 key is the normal choice now; a 4096-bit RSA key is not required.
- Browsers stopped showing the Extended Validation company name in the address bar in 2019, so an EV certificate no longer gives customers a visible sign.
- Public TLS certificates issued since 15 March 2026 are valid for at most 200 days, falling to 47 days in 2029, so renewal has to be automated (ACME).
- Turn on HSTS so that browsers never fall back to plain HTTP.
 A+ (Excellent)
- A (Very good)
 A- (Good)
- B (Acceptable)
 C (Weak)
- T (Certificate not trusted)
- F (Fail)
How I collected the grades
All the test results below were obtained publicly from SSL Labs. These results, published by the well-recognized security company Qualys, highlight issues in online banking security. My role was to explain the problems and provide solutions to ensure secure online banking. Additionally, I contacted all the mentioned banks via phone, Twitter, Facebook, and email to inform them of the issues that needed immediate resolution.

My recommendations for Oman banks
Some banks should consider using strong ciphers that support forward secrecy.
- All banks should generate a new certificate with a strong key (I recommended a 4096-bit RSA key then; RSA 2048-bit or ECDSA P-256 is the normal choice now).
- EV: an Extended Validation (EV) certificate is a certificate used for HTTPS websites and software that proves the legal entity controlling the website or software package. Obtaining an EV certificate requires verification of the requesting entity’s identity by a certificate authority (CA).
- Forward secrecy: in cryptography, forward secrecy (FS, also known as perfect forward secrecy) is a property of secure communication protocols in which compromise of long-term keys does not compromise past session keys. Forward secrecy protects past sessions against future compromises of secret keys or passwords.
Why a certificate is not trusted
There are many reasons why a certificate may not be trusted, and the report card shows the exact problem in bright red. Following the SSL Labs documentation, the problems fall into four categories.
1. Invalid certificate
A certificate is invalid if:
- it is used before its activation date;
- it is used after its expiry date;
- its hostnames don’t match the site’s hostname;
- it has been revoked.
2. Invalid configuration
In some cases, the certificate chain does not contain all the necessary certificates to connect the web server certificate to one of the root certificates in SSL Labs’ trust store. Less commonly, one of the certificates in the chain (other than the web server certificate) will have expired, and that invalidates the entire chain.
3. Unknown Certificate Authority
For trust to be established, SSL Labs must have the root certificate of the signing Certificate Authority in its trust store. SSL Labs does not maintain its own trust store; it uses the store maintained by Mozilla.
If SSL Labs marks a website as not trusted, that means that the average web user’s browser will not trust it either. For certain special groups of users, such websites can still be secure. For example, if you can securely verify that a self-signed website is operated by a person you trust, then you can trust that self-signed website too. Or, if you work for an organisation that manages its own trust, and you have its own root certificate already embedded in your browser. Such special cases do not work for the general public, however, and this is what SSL Labs shows on its report card.
4. Interoperability issues
In some rare cases, trust cannot be established because of interoperability issues between SSL Labs’ code and the code or configuration running on the server. SSL Labs reviews such cases by hand and asks you to contact it if you run into one: such problems are very difficult to troubleshoot, and the details you send may help find the root cause.
What these grades do not show
 Important Note and DISCLAIMER:
The contents of this blog do not relate in any way to a specific incident. This blog is especially not suggesting or even providing an argument that the recent card skimming going on in Oman is related to one of the aforementioned banks.
The specific tests that were run and discussed on this blog are for only one area of security, which emphasizes the strength of connection security between the end user and the bank via a web browser.
While some banks may not have ranked as strong as I had hoped on this test (a test that any person may perform themselves because it is publicly accessible), banks that rank lower on this test may rank higher on other tests. Banks can be very strong in other aspects of their security and their security as a whole cannot be determined based on a single test. Additionally, to test other aspects of security prior authorization by a specific bank is required, which this blog and the average person do not have.
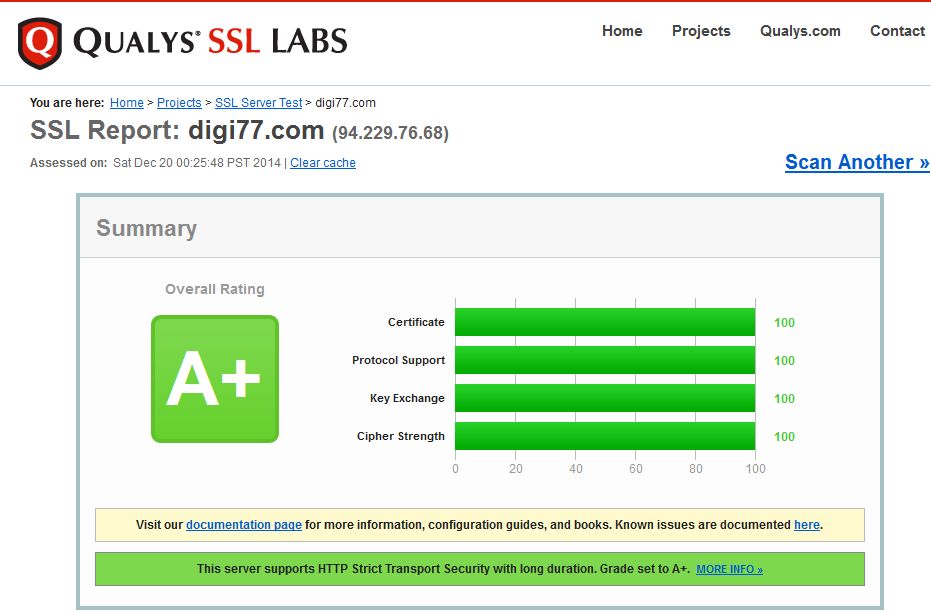
The SSL grade of digi77.com at the time
As we have seen, most of them failed to meet the security standards for SSL, which drives online banking. I believe that banks should always make sure that they maintain a grade of A+ as explained here.